Meet the Team at Logiq: Driving innovation in IT consultancy

Logiq News, as reported in Channel Eye on 24th January 2024


Meet the Team at Logiq: Driving innovation in IT consultancy

We were thrilled to be featured in the Channel Eye's 'Meet the Team' Series. They certainly dived right in!
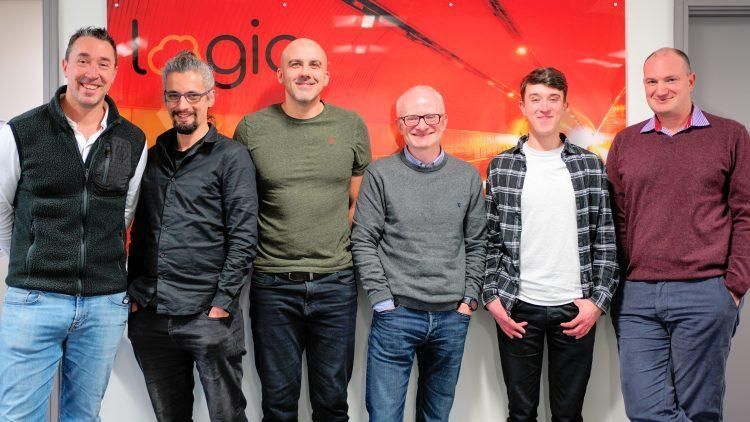
Welcome to our series, ‘Meet the Team’, where we meet the people behind the businesses in the Channel Islands to find out what they’re doing and what makes them tick. Today, we meet the dynamic team from IT Consultancy Logiq. 


Logiq, has a proven track record of delivering cutting-edge solutions to a diverse clientele where expertise meets innovation in the world of IT.


Our Services:

At Logiq we specialise in providing end-to-end IT consultancy services that encompass strategic planning, digital transformation, cybersecurity, and more. Our solutions are designed to optimise efficiency, enhance productivity, and drive sustainable growth for our clients.


New Office, New Beginnings:

It’s exciting times at Logiq as we’ve recently moved into our new offices.

The new space reflects our commitment to creating a collaborative and innovative work environment that fosters creativity and teamwork. The team are all really positive about their working environment which is so important!


The Team Dynamic:

Our team thrives on collaborative synergies, bringing together diverse skills and experiences to deliver top-tier solutions. The positive and dynamic work environment at Logiq is the secret ingredient behind our success.


Meet the Team:

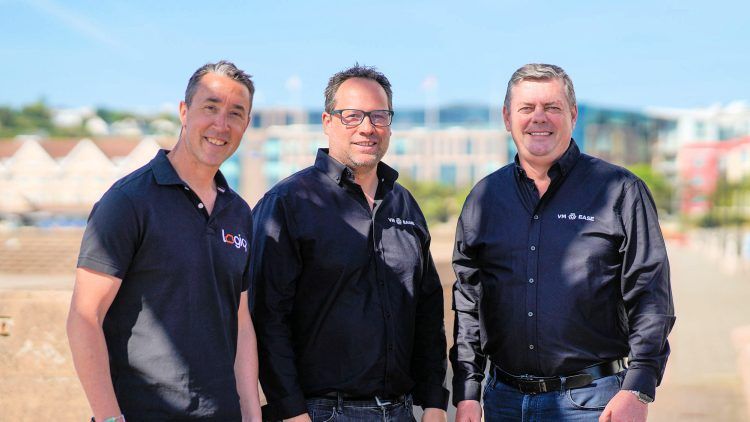
Giles Crouch – Founding Director

As a Founding Director, can you share the vision and values that inspired you to establish Logiq? How have these principles shaped the growth and success of Logiq in the dynamic world of IT consultancy? 

James and I formed Logiq out of a desire to provide the best levels of technical skills and experience to clients. We started Logiq with a global trust client working on technically complex migrations and integrations and have grown our client base from there. We will always stay true to our values of giving our clients the best levels of expertise and innovation.


James Hope – Founding Director

What do you find most rewarding about your role as Founding Director? Can you share moments or aspects of your responsibilities that bring the greatest satisfaction as a leader driving the success and vision of the company? 

I love working with people and the teamwork aspect of running a business the most.

I realise that a strong, happy, and healthy team is one of the best-selling points a company can have. Since our inception we have constantly planned ahead in terms of organising a growing business and essentially being more professional than our size would lend itself to. We are constantly evolving but the thing that we have been consistently passionate about is delivering excellent results for our clients. Personally, I have also realised, without knowing, that all those years in the RNLI have prepared me for working in a close knit, high performing team.

Giles Crouch and James Hope

Asa Venton – Senior Technical Consultant

Can you share a success story where you played a pivotal role in delivering exceptional results for a client? 

I played a crucial role in a successful cloud migration project for a client, overseeing the transition of their IT infrastructure to the cloud. Through careful planning, phased migration, and effective communication, we minimized disruptions, optimized performance, and achieved significant cost savings. The project’s success showcased my expertise in cloud architecture and project management.


Lee Shannon – Senior Technical Consultant

How does Logiq balance cutting-edge technology solutions with a personalised approach to meet the unique needs of each client? 

Logiq balances cutting-edge technology solutions with a personalised approach to meet the unique needs of each client by bringing together passionate and experienced technology experts. This combination allows us to really get to know each client and build an in depth understanding of their needs. This enables Logiq to deliver optimum, tailored solutions for each client.

Lee Shannon

Ross De la Mare – Technical Consultant

What aspects of your role as an IT Consultant do you find most rewarding? 

The aspects that I find rewarding within my role is being presented with a diverse range of environments and implementing a desired solution to move the client forward on many fronts.

While some of these solutions are somewhat standardised, there are often times where a tailored solution needs to be delivered which requires a lot of extra thought. Considering these requirements of the role and with technology always evolving, this keeps me engaged and always learning something new, which is also a bonus!


Emanuel Pontes – Junior Technical Consultant

What excites you most about the evolving landscape of technology? 

What excites me most about the evolution of technology is its boundless capacity for innovation and problem-solving. As a Microsoft Azure Administrator and a Certified Ethical Hacker (EC-Council), Azure exemplifies the power of cloud technology, utilizing immense computational capabilities to tackle real-world challenges with efficiency and creativity. Meanwhile in cybersecurity, the rapid pace of advancement is exhilarating. It goes beyond from just adapting to new threats; it’s about pushing the science, and the discovery that comes with that. For some people, technology is just a tool – for others it saves and changes lives.


Will Graham – Associate Technical Consultant

How do you stay ahead of the curve in terms of emerging technologies, and how does this commitment translate into providing innovative solutions for Logiq’s clients? 

Staying ahead of the curve in respect to emerging technologies is crucial in the fast-paced field of IT Consultancy. I ensure that I’m continuously learning and applying new technologies for the benefit of Logiq’s clients by:


  • Networking: I actively participate in professional networks, both online and offline. This includes attending industry conferences, joining relevant LinkedIn groups, and engaging with experts in the field. Networking provides insights into emerging technologies and their real-world applications.
  • Hands-on Experience: I believe hands-on experience with technology is key. I often set up personal projects to experiment with new tools and frameworks. This allows me to gain practical insights and troubleshoot potential challenges before implementing them in a client’s environment.
  • Beta-testing, trialling and Prototyping: I’m a strong advocate of beta-testing, trialling products and prototyping. This enables us to test new technologies in a controlled environment before recommending them to clients. It also fosters a mind-set of innovation and adaptability.


By adopting these strategies, I aim to not only stay ahead of the curve but also leverage emerging technologies effectively to provide innovative solutions that positively impact our clients’ businesses.


Conclusion:

We’re more than just an IT consultancy team; we’re the architects of your digital transformation – we deliver strategies that empower, technologies that enable, and partnerships that catalyse growth.


As we settle into our new offices, our commitment to excellence and client satisfaction remains unwavering.

If you’re ready to embark on a journey of innovation and progress and shape a future where technology propels you beyond limits, please contact us to discuss your needs.
October 26, 2026
We are thrilled to welcome Kyla McDonagh to Logiq as our newest Environment Care Specialist ! At Logiq, our Environment Care model is all about delivering proactive, meticulous support and keeping our clients’ digital estates secure, modern, and running smoothly. Kyla is stepping right into this mission, bringing a sharp technical mindset and fantastic energy to the team. A recent graduate in Computer Science with Artificial Intelligence from the University of Leeds, Kyla already has solid, hands-on experience under her belt - from large-scale corporate device deployments and cybersecurity operations in the local industry, to building advanced multi-agent security frameworks and AI-driven applications. Outside the world of tech, she’s equally dynamic - whether she's competing internationally on the water or instructing the next generation of sailors right here on the island. Her blend of curiosity, problem-solving drive, and dedication to high standards makes her a natural fit for Logiq. Please join us in giving Kyla a warm welcome to the team! We’re delighted to have you on board, Kyla. 👏
October 26, 2026
Lisa Barnes and Asa Venton will join James Hope as Giles Crouch steps down after more than six years as a director and shareholder to pursue his next venture.
October 26, 2026
Often, it’s when an organisation goes through rapid change. Whether that’s an acquisition, a carve-out, or untangling legacy systems under tight deadlines - it rarely feels structured, and most of the time it feels a lot like this picture. At Logiq, that tends to be when we get the call: when the technical challenges are messy, high-stakes, or time-critical, and a business needs an experienced pair of hands to step into the noise, bring order, and get things sorted. Looking back over the last few months, a few key projects stand out that reflect what the team here can actually take on: Business Carve-Out: We led the technical side of carving out a business unit—separating intertwined identities, data, and infrastructure so the new entity could operate cleanly on its own without breaking day-to-day operations. M&A Integration: Following an acquisition, we are handling the technical heavy lifting to bring two different businesses and their IT estates together under one coherent, secure setup. Complex Cloud Migration: We planned and executed an end-to-end cloud migration, transitioning legacy infrastructure and core workloads to modern cloud services with minimal friction and zero downtime. Large-Scale Azure Build via IaC: We’re currently architecting and deploying a major Microsoft Azure environment built entirely with Infrastructure as Code, making sure the foundation is automated, documented, and built to scale cleanly. Data Protection via Microsoft Purview DLP: We architected and deployed targeted Data Loss Prevention policies across sensitive environments, ensuring critical data is properly classified and protected without getting in the way of people doing their jobs. Forensic Response & Security Hardening: When urgent security risks arose, we carried out targeted forensic work to trace compromises and immediately rolled out hardened controls to secure the perimeter and lock down environments properly. Work like this isn't about following a generic script. It comes down to having experienced consultants who stay calm under pressure, understand the commercial realities, and know how to get the job done properly. Huge credit to the whole Logiq team for the work they put in behind the scenes, and thank you to the clients who trust us at such critical times. If you have a complex project coming up or need an experienced pair of hands on the technical side, get in touch.
October 26, 2026
For decades, business leaders have been comforted by a comforting, expensive lie: that if you spend enough money on a big enough digital wall, your business is safe. We bought into the medieval castle analogy. We treated corporate IT security as a perimeter exercise. You build a deep moat, erect thick walls in the form of firewalls, secure office networks, and gated server rooms; then you assume that everything inside those walls is safe, and everything outside is hostile. It was a neat, easily understood concept. It was also completely dismantled years ago. If you are still managing your business risk based on the idea of a secure perimeter, you aren't just behind the times - you are actively leaving the back door wide open. In a world defined by hybrid working, cloud-based applications, and mobile devices, the castle walls haven’t just been breached; they have dissolved entirely. Your data is already outside the moat. It’s on a laptop in a coffee shop, it’s in a SaaS platform hosted halfway across the world, and it’s being accessed by employees on their personal phones. The threat landscape has evolved. It’s time corporate security caught up. The Illusion of the Safe Insider The most uncomfortable truth in modern cyber security is that the biggest vulnerability to your business isn’t a shadowy syndicate of state-sponsored hackers trying to blast through your external defences. It is standard, day-to-day operational reality. When a breach occurs, it is rarely because a firewall failed. It is almost always because a well-meaning employee, sitting comfortably inside your trusted environment, clicked a highly sophisticated phishing link, reused a compromised password, or accidentally shared a sensitive folder with an external party. The traditional model treats anyone inside the network as inherently trustworthy. That is a fatal flaw. Once an attacker compromises a single user identity, they don’t need to break into your system; they can simply log in. From there, they can move laterally across your entire infrastructure, accessing unrestricted files, financial data, and client records because no one is checking their credentials twice. This is why the old way of thinking is dead. True cyber resilience isn't about guarding the border; it’s about protecting the data itself, regardless of where it travels, who is holding it, or what time of day it is accessed. Shift the Mindset: Never Trust, Always Verify To survive in this environment, businesses have to embrace a much more unsentimental approach to their technology. In the industry, we call this a "Zero Trust" framework, but stripped of the marketing jargon, it boils down to a simple operational principle: Never trust, always verify. It means treating every single request for access, whether it comes from the CEO sitting at their desk in HQ or a junior administrator working from home, with the exact same level of healthy suspicion. To achieve this, the focus of your IT strategy has to shift away from reactive firefighting and onto continuous, rigorous hardening of the environment. This isn’t a one-off software purchase; it is a relentless operational discipline. It relies on three non-negotiable pillars: Ruthless Identity Management: Multi-factor authentication (MFA) is no longer a luxury; it is the bare minimum. True security requires conditional access rules that evaluate the context of a login. If an account attempts to access sensitive financial data from an unrecognized device in a different country, the system should block it automatically, no questions asked. Device Health Verification: You cannot allow unmanaged, unhardened devices to touch corporate data. Before a laptop or phone is granted access to your network, the system must verify that it is fully patched, encrypted, and compliant with strict security baselines. If it isn't, it stays outside. Granular Data Governance: You cannot protect what you do don’t know you have. Businesses must have absolute visibility over their data lifecycles. This means classifying sensitive information, restricting access to only those who strictly need it to do their jobs, and ensuring that data cannot be copied, downloaded, or leaked; even if a user account is compromised. Security as a Competitive Edge There is a common misconception among directors that tightening security controls inherently introduces friction, slowing down operations and frustrating staff. The reality is exactly the opposite. Weak, chaotic infrastructure is what creates friction. When you don’t trust your environment, you build clumsy, bureaucratic roadblocks to compensate. Conversely, when you have absolute control and visibility over your data, you gain operational freedom. A fully hardened, compliant environment allows a business to scale with confidence, adopt new cloud technologies safely, and pass stringent client security audits without scrambling. It transforms cyber security from a grudge insurance expense into a genuine competitive advantage. A Question for the Boardroom Technology moves at a staggering pace, but the fundamental responsibility of governance remains unchanged. As business leaders, the fiduciary duty to protect client data, intellectual property, and corporate reputation rests squarely with us. The next time you review your risk register or sign off on an IT budget, look past the line items for firewalls and antivirus software. Ask your technical teams a deeper, more uncomfortable question: “If our perimeter failed entirely this afternoon, how safe is our actual data?”  If the answer takes more than a few seconds to explain, you already know you have work to do.
VMease and Logiq partner to deliver sovereign, cost-effective private cloud solutions
By Channel Eye • May 27, 2026
The partnership brings together VMease’s private cloud platform with Logiq’s expertise in infrastructure, cloud transformation and managed services. The combined offering is designed to help organisations reduce reliance on legacy virtualisation platforms, lower costs and simplify operations at a time when many busines
October 26, 2026
We are thrilled to welcome Kyla McDonagh to Logiq as our newest Environment Care Specialist ! At Logiq, our Environment Care model is all about delivering proactive, meticulous support and keeping our clients’ digital estates secure, modern, and running smoothly. Kyla is stepping right into this mission, bringing a sharp technical mindset and fantastic energy to the team. A recent graduate in Computer Science with Artificial Intelligence from the University of Leeds, Kyla already has solid, hands-on experience under her belt - from large-scale corporate device deployments and cybersecurity operations in the local industry, to building advanced multi-agent security frameworks and AI-driven applications. Outside the world of tech, she’s equally dynamic - whether she's competing internationally on the water or instructing the next generation of sailors right here on the island. Her blend of curiosity, problem-solving drive, and dedication to high standards makes her a natural fit for Logiq. Please join us in giving Kyla a warm welcome to the team! We’re delighted to have you on board, Kyla. 👏
October 26, 2026
Lisa Barnes and Asa Venton will join James Hope as Giles Crouch steps down after more than six years as a director and shareholder to pursue his next venture.
October 26, 2026
Often, it’s when an organisation goes through rapid change. Whether that’s an acquisition, a carve-out, or untangling legacy systems under tight deadlines - it rarely feels structured, and most of the time it feels a lot like this picture. At Logiq, that tends to be when we get the call: when the technical challenges are messy, high-stakes, or time-critical, and a business needs an experienced pair of hands to step into the noise, bring order, and get things sorted. Looking back over the last few months, a few key projects stand out that reflect what the team here can actually take on: Business Carve-Out: We led the technical side of carving out a business unit—separating intertwined identities, data, and infrastructure so the new entity could operate cleanly on its own without breaking day-to-day operations. M&A Integration: Following an acquisition, we are handling the technical heavy lifting to bring two different businesses and their IT estates together under one coherent, secure setup. Complex Cloud Migration: We planned and executed an end-to-end cloud migration, transitioning legacy infrastructure and core workloads to modern cloud services with minimal friction and zero downtime. Large-Scale Azure Build via IaC: We’re currently architecting and deploying a major Microsoft Azure environment built entirely with Infrastructure as Code, making sure the foundation is automated, documented, and built to scale cleanly. Data Protection via Microsoft Purview DLP: We architected and deployed targeted Data Loss Prevention policies across sensitive environments, ensuring critical data is properly classified and protected without getting in the way of people doing their jobs. Forensic Response & Security Hardening: When urgent security risks arose, we carried out targeted forensic work to trace compromises and immediately rolled out hardened controls to secure the perimeter and lock down environments properly. Work like this isn't about following a generic script. It comes down to having experienced consultants who stay calm under pressure, understand the commercial realities, and know how to get the job done properly. Huge credit to the whole Logiq team for the work they put in behind the scenes, and thank you to the clients who trust us at such critical times. If you have a complex project coming up or need an experienced pair of hands on the technical side, get in touch.
October 26, 2026
For decades, business leaders have been comforted by a comforting, expensive lie: that if you spend enough money on a big enough digital wall, your business is safe. We bought into the medieval castle analogy. We treated corporate IT security as a perimeter exercise. You build a deep moat, erect thick walls in the form of firewalls, secure office networks, and gated server rooms; then you assume that everything inside those walls is safe, and everything outside is hostile. It was a neat, easily understood concept. It was also completely dismantled years ago. If you are still managing your business risk based on the idea of a secure perimeter, you aren't just behind the times - you are actively leaving the back door wide open. In a world defined by hybrid working, cloud-based applications, and mobile devices, the castle walls haven’t just been breached; they have dissolved entirely. Your data is already outside the moat. It’s on a laptop in a coffee shop, it’s in a SaaS platform hosted halfway across the world, and it’s being accessed by employees on their personal phones. The threat landscape has evolved. It’s time corporate security caught up. The Illusion of the Safe Insider The most uncomfortable truth in modern cyber security is that the biggest vulnerability to your business isn’t a shadowy syndicate of state-sponsored hackers trying to blast through your external defences. It is standard, day-to-day operational reality. When a breach occurs, it is rarely because a firewall failed. It is almost always because a well-meaning employee, sitting comfortably inside your trusted environment, clicked a highly sophisticated phishing link, reused a compromised password, or accidentally shared a sensitive folder with an external party. The traditional model treats anyone inside the network as inherently trustworthy. That is a fatal flaw. Once an attacker compromises a single user identity, they don’t need to break into your system; they can simply log in. From there, they can move laterally across your entire infrastructure, accessing unrestricted files, financial data, and client records because no one is checking their credentials twice. This is why the old way of thinking is dead. True cyber resilience isn't about guarding the border; it’s about protecting the data itself, regardless of where it travels, who is holding it, or what time of day it is accessed. Shift the Mindset: Never Trust, Always Verify To survive in this environment, businesses have to embrace a much more unsentimental approach to their technology. In the industry, we call this a "Zero Trust" framework, but stripped of the marketing jargon, it boils down to a simple operational principle: Never trust, always verify. It means treating every single request for access, whether it comes from the CEO sitting at their desk in HQ or a junior administrator working from home, with the exact same level of healthy suspicion. To achieve this, the focus of your IT strategy has to shift away from reactive firefighting and onto continuous, rigorous hardening of the environment. This isn’t a one-off software purchase; it is a relentless operational discipline. It relies on three non-negotiable pillars: Ruthless Identity Management: Multi-factor authentication (MFA) is no longer a luxury; it is the bare minimum. True security requires conditional access rules that evaluate the context of a login. If an account attempts to access sensitive financial data from an unrecognized device in a different country, the system should block it automatically, no questions asked. Device Health Verification: You cannot allow unmanaged, unhardened devices to touch corporate data. Before a laptop or phone is granted access to your network, the system must verify that it is fully patched, encrypted, and compliant with strict security baselines. If it isn't, it stays outside. Granular Data Governance: You cannot protect what you do don’t know you have. Businesses must have absolute visibility over their data lifecycles. This means classifying sensitive information, restricting access to only those who strictly need it to do their jobs, and ensuring that data cannot be copied, downloaded, or leaked; even if a user account is compromised. Security as a Competitive Edge There is a common misconception among directors that tightening security controls inherently introduces friction, slowing down operations and frustrating staff. The reality is exactly the opposite. Weak, chaotic infrastructure is what creates friction. When you don’t trust your environment, you build clumsy, bureaucratic roadblocks to compensate. Conversely, when you have absolute control and visibility over your data, you gain operational freedom. A fully hardened, compliant environment allows a business to scale with confidence, adopt new cloud technologies safely, and pass stringent client security audits without scrambling. It transforms cyber security from a grudge insurance expense into a genuine competitive advantage. A Question for the Boardroom Technology moves at a staggering pace, but the fundamental responsibility of governance remains unchanged. As business leaders, the fiduciary duty to protect client data, intellectual property, and corporate reputation rests squarely with us. The next time you review your risk register or sign off on an IT budget, look past the line items for firewalls and antivirus software. Ask your technical teams a deeper, more uncomfortable question: “If our perimeter failed entirely this afternoon, how safe is our actual data?”  If the answer takes more than a few seconds to explain, you already know you have work to do.
VMease and Logiq partner to deliver sovereign, cost-effective private cloud solutions
By Channel Eye • May 27, 2026
The partnership brings together VMease’s private cloud platform with Logiq’s expertise in infrastructure, cloud transformation and managed services. The combined offering is designed to help organisations reduce reliance on legacy virtualisation platforms, lower costs and simplify operations at a time when many busines
Are you treading water...? Or is technology driving your business?
By Logiq • March 13, 2026
It’s 2026, and we’re beyond the stage where "digital transformation" is a buzzword. By now, it’s a basic requirement. Yet we still see many firms stuck in a reactive loop of fixing things only when they break rather than using technology to get ahead.
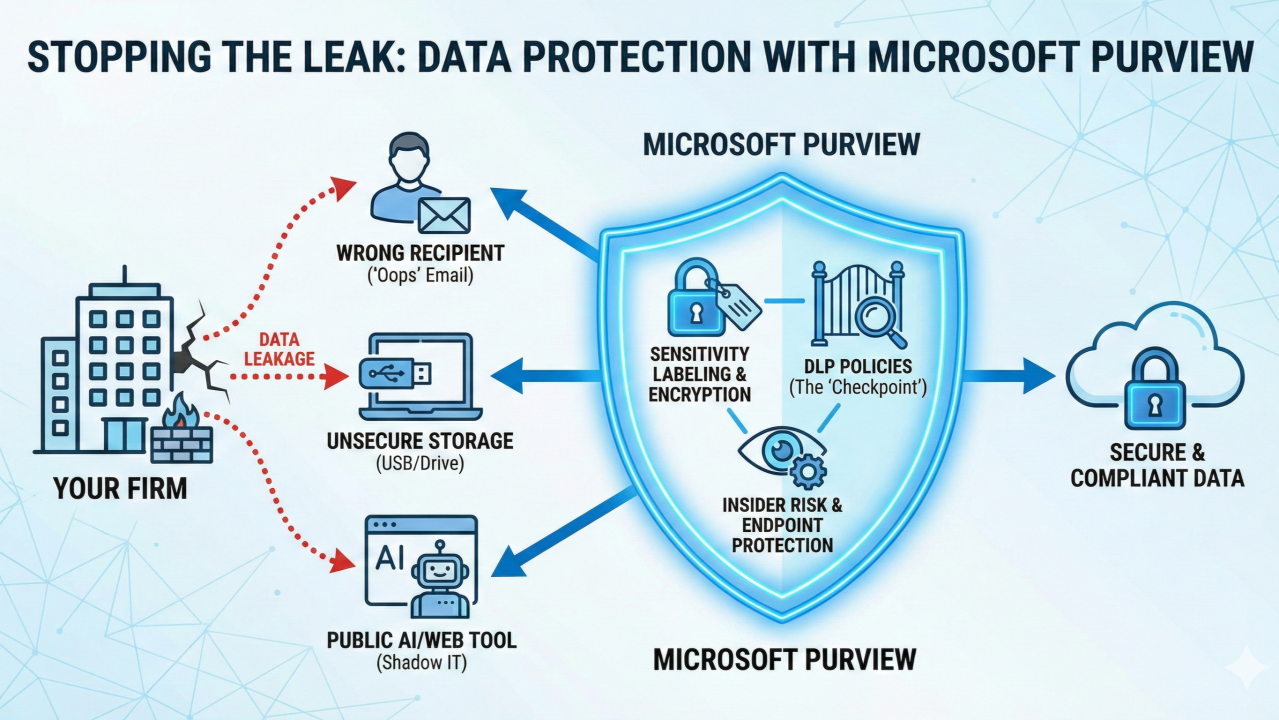
Data-protection-with-Microsoft-Purview
By Logiq • January 21, 2026
Most businesses we work with have sensible tooling in place to protect themselves from the outside. You’ve likely got the email filtering, web protection, anti-virus, vulnerability management, and encryption all sorted. But the uncomfortable question we often have to ask is: What are you doing to stop data being leake
Financial businesses need to comply with new digital regulation
By Channel Eye Media • December 16, 2024
Channel Eye Article Featuring Logiq
Is the thought of protecting your artefacts in Microsoft 365 giving you sleepless nights?
By Logiq • June 26, 2024
Many companies in recent years have adopted the move to Microsoft 365 and are left wondering why the Microsoft options for protecting their data fall a little short. Logiq have partnered with Veeam, and as an existing Microsoft Partner, we have real-world experience of how these shortfalls can be filled.
Do employees truly grasp their crucial role in maintaining IT security?
By Logiq • May 26, 2024
In today's rapidly evolving digital landscape, organisations are investing heavily in cutting-edge software, robust hardware, and comprehensive policies and procedures to ensure compliance with industry standards and security frameworks.