Exciting news from the Logiq team! 🚀

We are thrilled to welcome Kyla McDonagh to Logiq as our newest Environment Care Specialist!
 
At Logiq, our Environment Care model is all about delivering proactive, meticulous support and keeping our clients’ digital estates secure, modern, and running smoothly. Kyla is stepping right into this mission, bringing a sharp technical mindset and fantastic energy to the team.
A recent graduate in
Computer Science with Artificial Intelligence from the University of Leeds, Kyla already has solid, hands-on experience under her belt - from large-scale corporate device deployments and cybersecurity operations in the local industry, to building advanced multi-agent security frameworks and AI-driven applications.
 
Outside the world of tech, she’s equally dynamic - whether she's competing internationally on the water or instructing the next generation of sailors right here on the island.
 
Her blend of curiosity, problem-solving drive, and dedication to high standards makes her a natural fit for Logiq.
 
Please join us in giving Kyla a warm welcome to the team! We’re delighted to have you on board, Kyla. 👏

October 26, 2026
Lisa Barnes and Asa Venton will join James Hope as Giles Crouch steps down after more than six years as a director and shareholder to pursue his next venture.
October 26, 2026
Often, it’s when an organisation goes through rapid change. Whether that’s an acquisition, a carve-out, or untangling legacy systems under tight deadlines - it rarely feels structured, and most of the time it feels a lot like this picture. At Logiq, that tends to be when we get the call: when the technical challenges are messy, high-stakes, or time-critical, and a business needs an experienced pair of hands to step into the noise, bring order, and get things sorted. Looking back over the last few months, a few key projects stand out that reflect what the team here can actually take on: Business Carve-Out: We led the technical side of carving out a business unit—separating intertwined identities, data, and infrastructure so the new entity could operate cleanly on its own without breaking day-to-day operations. M&A Integration: Following an acquisition, we are handling the technical heavy lifting to bring two different businesses and their IT estates together under one coherent, secure setup. Complex Cloud Migration: We planned and executed an end-to-end cloud migration, transitioning legacy infrastructure and core workloads to modern cloud services with minimal friction and zero downtime. Large-Scale Azure Build via IaC: We’re currently architecting and deploying a major Microsoft Azure environment built entirely with Infrastructure as Code, making sure the foundation is automated, documented, and built to scale cleanly. Data Protection via Microsoft Purview DLP: We architected and deployed targeted Data Loss Prevention policies across sensitive environments, ensuring critical data is properly classified and protected without getting in the way of people doing their jobs. Forensic Response & Security Hardening: When urgent security risks arose, we carried out targeted forensic work to trace compromises and immediately rolled out hardened controls to secure the perimeter and lock down environments properly. Work like this isn't about following a generic script. It comes down to having experienced consultants who stay calm under pressure, understand the commercial realities, and know how to get the job done properly. Huge credit to the whole Logiq team for the work they put in behind the scenes, and thank you to the clients who trust us at such critical times. If you have a complex project coming up or need an experienced pair of hands on the technical side, get in touch.
October 26, 2026
For decades, business leaders have been comforted by a comforting, expensive lie: that if you spend enough money on a big enough digital wall, your business is safe. We bought into the medieval castle analogy. We treated corporate IT security as a perimeter exercise. You build a deep moat, erect thick walls in the form of firewalls, secure office networks, and gated server rooms; then you assume that everything inside those walls is safe, and everything outside is hostile. It was a neat, easily understood concept. It was also completely dismantled years ago. If you are still managing your business risk based on the idea of a secure perimeter, you aren't just behind the times - you are actively leaving the back door wide open. In a world defined by hybrid working, cloud-based applications, and mobile devices, the castle walls haven’t just been breached; they have dissolved entirely. Your data is already outside the moat. It’s on a laptop in a coffee shop, it’s in a SaaS platform hosted halfway across the world, and it’s being accessed by employees on their personal phones. The threat landscape has evolved. It’s time corporate security caught up. The Illusion of the Safe Insider The most uncomfortable truth in modern cyber security is that the biggest vulnerability to your business isn’t a shadowy syndicate of state-sponsored hackers trying to blast through your external defences. It is standard, day-to-day operational reality. When a breach occurs, it is rarely because a firewall failed. It is almost always because a well-meaning employee, sitting comfortably inside your trusted environment, clicked a highly sophisticated phishing link, reused a compromised password, or accidentally shared a sensitive folder with an external party. The traditional model treats anyone inside the network as inherently trustworthy. That is a fatal flaw. Once an attacker compromises a single user identity, they don’t need to break into your system; they can simply log in. From there, they can move laterally across your entire infrastructure, accessing unrestricted files, financial data, and client records because no one is checking their credentials twice. This is why the old way of thinking is dead. True cyber resilience isn't about guarding the border; it’s about protecting the data itself, regardless of where it travels, who is holding it, or what time of day it is accessed. Shift the Mindset: Never Trust, Always Verify To survive in this environment, businesses have to embrace a much more unsentimental approach to their technology. In the industry, we call this a "Zero Trust" framework, but stripped of the marketing jargon, it boils down to a simple operational principle: Never trust, always verify. It means treating every single request for access, whether it comes from the CEO sitting at their desk in HQ or a junior administrator working from home, with the exact same level of healthy suspicion. To achieve this, the focus of your IT strategy has to shift away from reactive firefighting and onto continuous, rigorous hardening of the environment. This isn’t a one-off software purchase; it is a relentless operational discipline. It relies on three non-negotiable pillars: Ruthless Identity Management: Multi-factor authentication (MFA) is no longer a luxury; it is the bare minimum. True security requires conditional access rules that evaluate the context of a login. If an account attempts to access sensitive financial data from an unrecognized device in a different country, the system should block it automatically, no questions asked. Device Health Verification: You cannot allow unmanaged, unhardened devices to touch corporate data. Before a laptop or phone is granted access to your network, the system must verify that it is fully patched, encrypted, and compliant with strict security baselines. If it isn't, it stays outside. Granular Data Governance: You cannot protect what you do don’t know you have. Businesses must have absolute visibility over their data lifecycles. This means classifying sensitive information, restricting access to only those who strictly need it to do their jobs, and ensuring that data cannot be copied, downloaded, or leaked; even if a user account is compromised. Security as a Competitive Edge There is a common misconception among directors that tightening security controls inherently introduces friction, slowing down operations and frustrating staff. The reality is exactly the opposite. Weak, chaotic infrastructure is what creates friction. When you don’t trust your environment, you build clumsy, bureaucratic roadblocks to compensate. Conversely, when you have absolute control and visibility over your data, you gain operational freedom. A fully hardened, compliant environment allows a business to scale with confidence, adopt new cloud technologies safely, and pass stringent client security audits without scrambling. It transforms cyber security from a grudge insurance expense into a genuine competitive advantage. A Question for the Boardroom Technology moves at a staggering pace, but the fundamental responsibility of governance remains unchanged. As business leaders, the fiduciary duty to protect client data, intellectual property, and corporate reputation rests squarely with us. The next time you review your risk register or sign off on an IT budget, look past the line items for firewalls and antivirus software. Ask your technical teams a deeper, more uncomfortable question: “If our perimeter failed entirely this afternoon, how safe is our actual data?”  If the answer takes more than a few seconds to explain, you already know you have work to do.
VMease and Logiq partner to deliver sovereign, cost-effective private cloud solutions
By Channel Eye • May 27, 2026
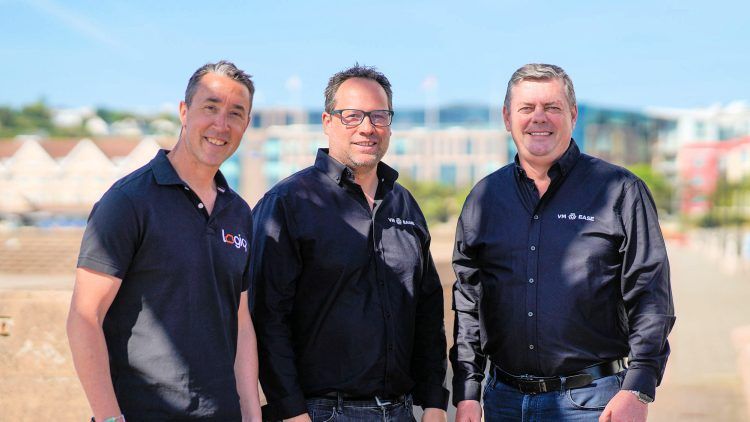
The partnership brings together VMease’s private cloud platform with Logiq’s expertise in infrastructure, cloud transformation and managed services. The combined offering is designed to help organisations reduce reliance on legacy virtualisation platforms, lower costs and simplify operations at a time when many busines
Are you treading water...? Or is technology driving your business?
By Logiq • March 13, 2026
It’s 2026, and we’re beyond the stage where "digital transformation" is a buzzword. By now, it’s a basic requirement. Yet we still see many firms stuck in a reactive loop of fixing things only when they break rather than using technology to get ahead.
October 26, 2026
Lisa Barnes and Asa Venton will join James Hope as Giles Crouch steps down after more than six years as a director and shareholder to pursue his next venture.
October 26, 2026
Often, it’s when an organisation goes through rapid change. Whether that’s an acquisition, a carve-out, or untangling legacy systems under tight deadlines - it rarely feels structured, and most of the time it feels a lot like this picture. At Logiq, that tends to be when we get the call: when the technical challenges are messy, high-stakes, or time-critical, and a business needs an experienced pair of hands to step into the noise, bring order, and get things sorted. Looking back over the last few months, a few key projects stand out that reflect what the team here can actually take on: Business Carve-Out: We led the technical side of carving out a business unit—separating intertwined identities, data, and infrastructure so the new entity could operate cleanly on its own without breaking day-to-day operations. M&A Integration: Following an acquisition, we are handling the technical heavy lifting to bring two different businesses and their IT estates together under one coherent, secure setup. Complex Cloud Migration: We planned and executed an end-to-end cloud migration, transitioning legacy infrastructure and core workloads to modern cloud services with minimal friction and zero downtime. Large-Scale Azure Build via IaC: We’re currently architecting and deploying a major Microsoft Azure environment built entirely with Infrastructure as Code, making sure the foundation is automated, documented, and built to scale cleanly. Data Protection via Microsoft Purview DLP: We architected and deployed targeted Data Loss Prevention policies across sensitive environments, ensuring critical data is properly classified and protected without getting in the way of people doing their jobs. Forensic Response & Security Hardening: When urgent security risks arose, we carried out targeted forensic work to trace compromises and immediately rolled out hardened controls to secure the perimeter and lock down environments properly. Work like this isn't about following a generic script. It comes down to having experienced consultants who stay calm under pressure, understand the commercial realities, and know how to get the job done properly. Huge credit to the whole Logiq team for the work they put in behind the scenes, and thank you to the clients who trust us at such critical times. If you have a complex project coming up or need an experienced pair of hands on the technical side, get in touch.
October 26, 2026
For decades, business leaders have been comforted by a comforting, expensive lie: that if you spend enough money on a big enough digital wall, your business is safe. We bought into the medieval castle analogy. We treated corporate IT security as a perimeter exercise. You build a deep moat, erect thick walls in the form of firewalls, secure office networks, and gated server rooms; then you assume that everything inside those walls is safe, and everything outside is hostile. It was a neat, easily understood concept. It was also completely dismantled years ago. If you are still managing your business risk based on the idea of a secure perimeter, you aren't just behind the times - you are actively leaving the back door wide open. In a world defined by hybrid working, cloud-based applications, and mobile devices, the castle walls haven’t just been breached; they have dissolved entirely. Your data is already outside the moat. It’s on a laptop in a coffee shop, it’s in a SaaS platform hosted halfway across the world, and it’s being accessed by employees on their personal phones. The threat landscape has evolved. It’s time corporate security caught up. The Illusion of the Safe Insider The most uncomfortable truth in modern cyber security is that the biggest vulnerability to your business isn’t a shadowy syndicate of state-sponsored hackers trying to blast through your external defences. It is standard, day-to-day operational reality. When a breach occurs, it is rarely because a firewall failed. It is almost always because a well-meaning employee, sitting comfortably inside your trusted environment, clicked a highly sophisticated phishing link, reused a compromised password, or accidentally shared a sensitive folder with an external party. The traditional model treats anyone inside the network as inherently trustworthy. That is a fatal flaw. Once an attacker compromises a single user identity, they don’t need to break into your system; they can simply log in. From there, they can move laterally across your entire infrastructure, accessing unrestricted files, financial data, and client records because no one is checking their credentials twice. This is why the old way of thinking is dead. True cyber resilience isn't about guarding the border; it’s about protecting the data itself, regardless of where it travels, who is holding it, or what time of day it is accessed. Shift the Mindset: Never Trust, Always Verify To survive in this environment, businesses have to embrace a much more unsentimental approach to their technology. In the industry, we call this a "Zero Trust" framework, but stripped of the marketing jargon, it boils down to a simple operational principle: Never trust, always verify. It means treating every single request for access, whether it comes from the CEO sitting at their desk in HQ or a junior administrator working from home, with the exact same level of healthy suspicion. To achieve this, the focus of your IT strategy has to shift away from reactive firefighting and onto continuous, rigorous hardening of the environment. This isn’t a one-off software purchase; it is a relentless operational discipline. It relies on three non-negotiable pillars: Ruthless Identity Management: Multi-factor authentication (MFA) is no longer a luxury; it is the bare minimum. True security requires conditional access rules that evaluate the context of a login. If an account attempts to access sensitive financial data from an unrecognized device in a different country, the system should block it automatically, no questions asked. Device Health Verification: You cannot allow unmanaged, unhardened devices to touch corporate data. Before a laptop or phone is granted access to your network, the system must verify that it is fully patched, encrypted, and compliant with strict security baselines. If it isn't, it stays outside. Granular Data Governance: You cannot protect what you do don’t know you have. Businesses must have absolute visibility over their data lifecycles. This means classifying sensitive information, restricting access to only those who strictly need it to do their jobs, and ensuring that data cannot be copied, downloaded, or leaked; even if a user account is compromised. Security as a Competitive Edge There is a common misconception among directors that tightening security controls inherently introduces friction, slowing down operations and frustrating staff. The reality is exactly the opposite. Weak, chaotic infrastructure is what creates friction. When you don’t trust your environment, you build clumsy, bureaucratic roadblocks to compensate. Conversely, when you have absolute control and visibility over your data, you gain operational freedom. A fully hardened, compliant environment allows a business to scale with confidence, adopt new cloud technologies safely, and pass stringent client security audits without scrambling. It transforms cyber security from a grudge insurance expense into a genuine competitive advantage. A Question for the Boardroom Technology moves at a staggering pace, but the fundamental responsibility of governance remains unchanged. As business leaders, the fiduciary duty to protect client data, intellectual property, and corporate reputation rests squarely with us. The next time you review your risk register or sign off on an IT budget, look past the line items for firewalls and antivirus software. Ask your technical teams a deeper, more uncomfortable question: “If our perimeter failed entirely this afternoon, how safe is our actual data?”  If the answer takes more than a few seconds to explain, you already know you have work to do.
VMease and Logiq partner to deliver sovereign, cost-effective private cloud solutions
By Channel Eye • May 27, 2026
The partnership brings together VMease’s private cloud platform with Logiq’s expertise in infrastructure, cloud transformation and managed services. The combined offering is designed to help organisations reduce reliance on legacy virtualisation platforms, lower costs and simplify operations at a time when many busines
Are you treading water...? Or is technology driving your business?
By Logiq • March 13, 2026
It’s 2026, and we’re beyond the stage where "digital transformation" is a buzzword. By now, it’s a basic requirement. Yet we still see many firms stuck in a reactive loop of fixing things only when they break rather than using technology to get ahead.
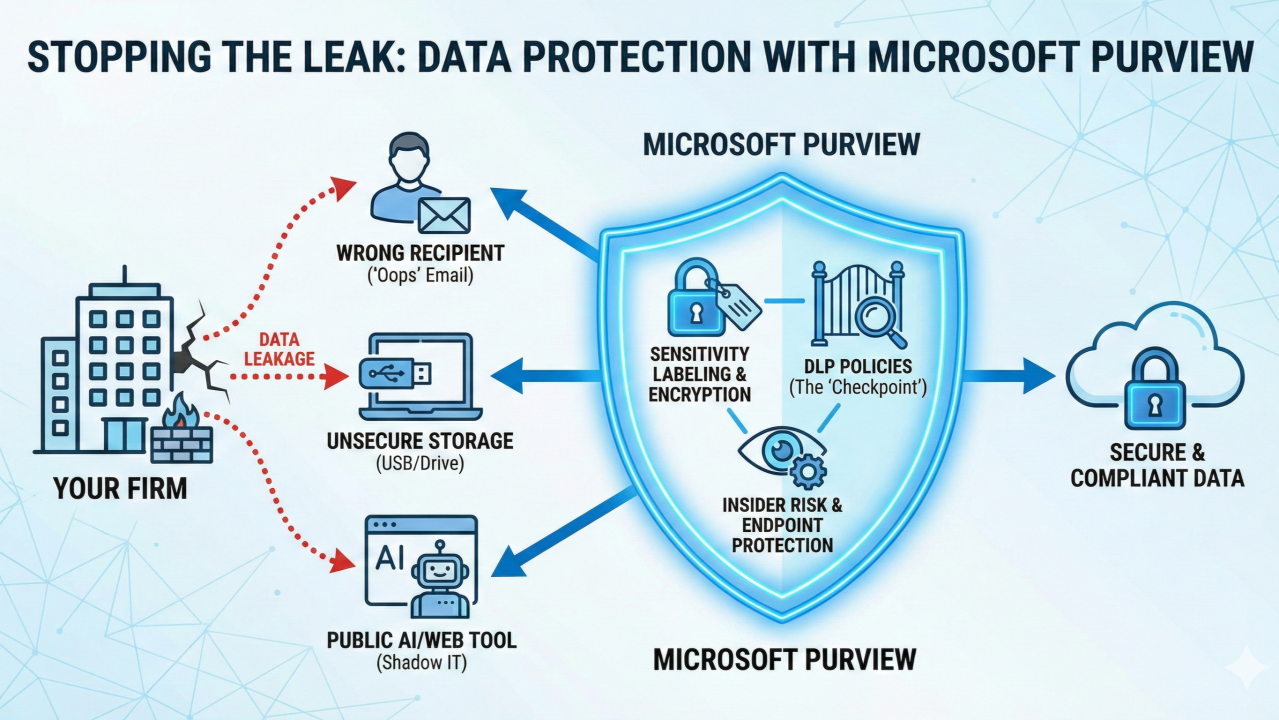
Data-protection-with-Microsoft-Purview
By Logiq • January 21, 2026
Most businesses we work with have sensible tooling in place to protect themselves from the outside. You’ve likely got the email filtering, web protection, anti-virus, vulnerability management, and encryption all sorted. But the uncomfortable question we often have to ask is: What are you doing to stop data being leake
Financial businesses need to comply with new digital regulation
By Channel Eye Media • December 16, 2024
Channel Eye Article Featuring Logiq
Is the thought of protecting your artefacts in Microsoft 365 giving you sleepless nights?
By Logiq • June 26, 2024
Many companies in recent years have adopted the move to Microsoft 365 and are left wondering why the Microsoft options for protecting their data fall a little short. Logiq have partnered with Veeam, and as an existing Microsoft Partner, we have real-world experience of how these shortfalls can be filled.
Do employees truly grasp their crucial role in maintaining IT security?
By Logiq • May 26, 2024
In today's rapidly evolving digital landscape, organisations are investing heavily in cutting-edge software, robust hardware, and comprehensive policies and procedures to ensure compliance with industry standards and security frameworks.
How often do you ensure your company's computer systems has all the latest updates installed?
By Logiq • April 26, 2024
In today's digital landscape, where cyber-attacks are becoming increasingly sophisticated, it's crucial to prioritize the security of your computer systems and network.